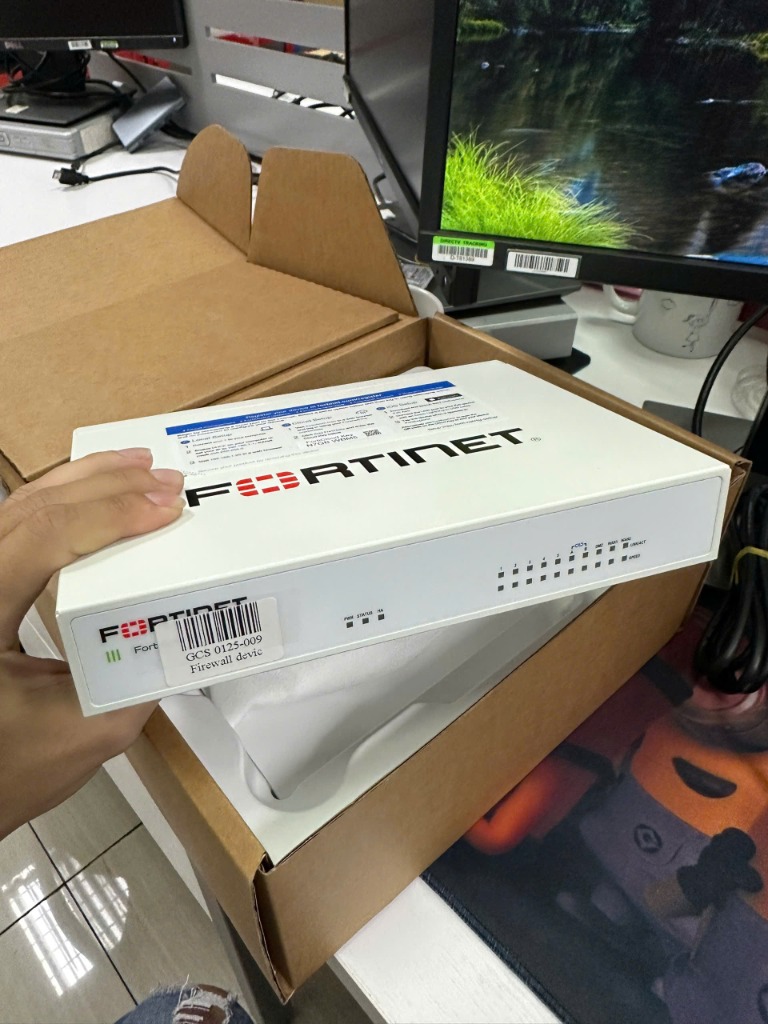
On-Premises Network Security & VPN
Next-Gen Firewalls & Enterprise Datacenter Infrastructure
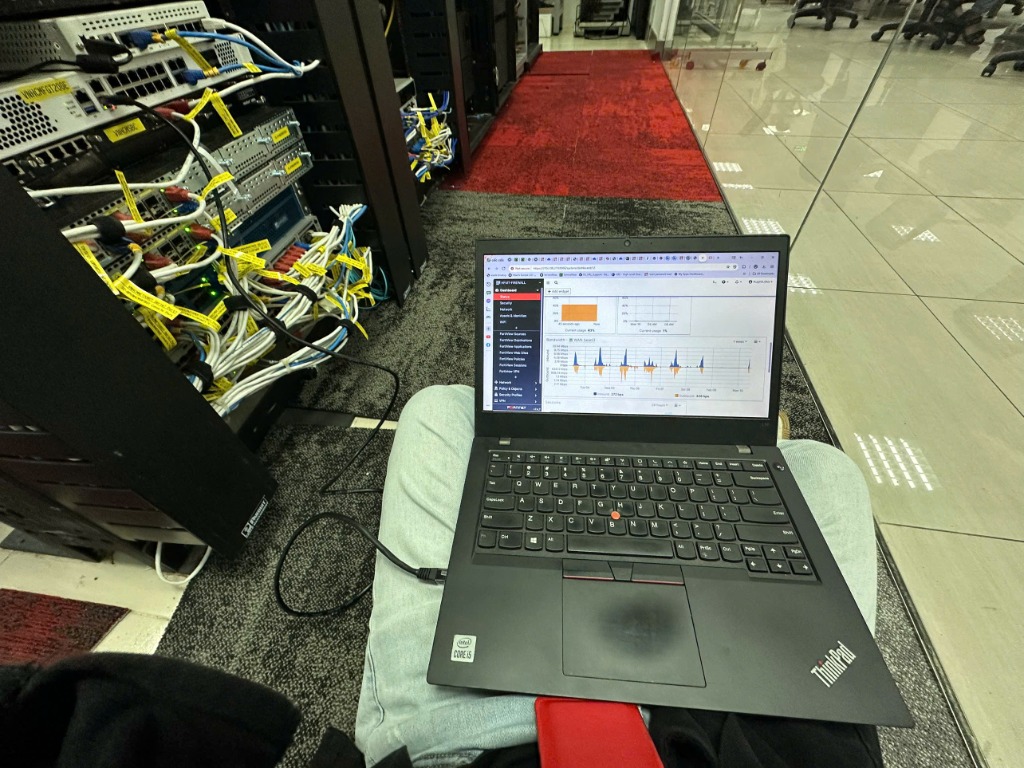
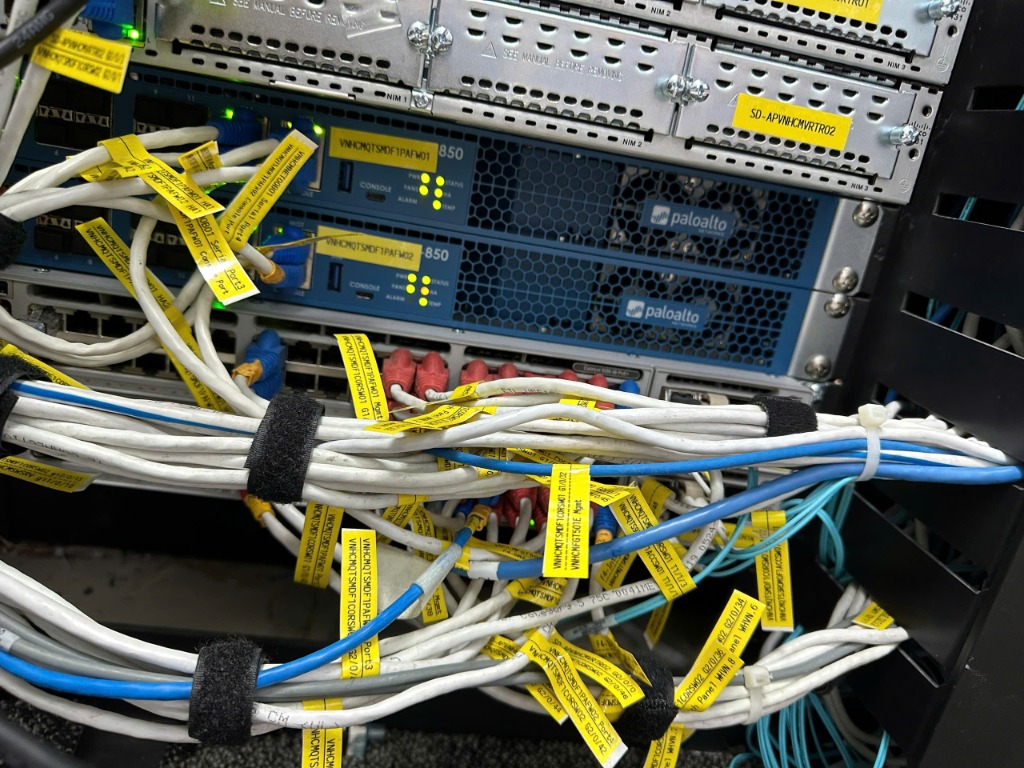
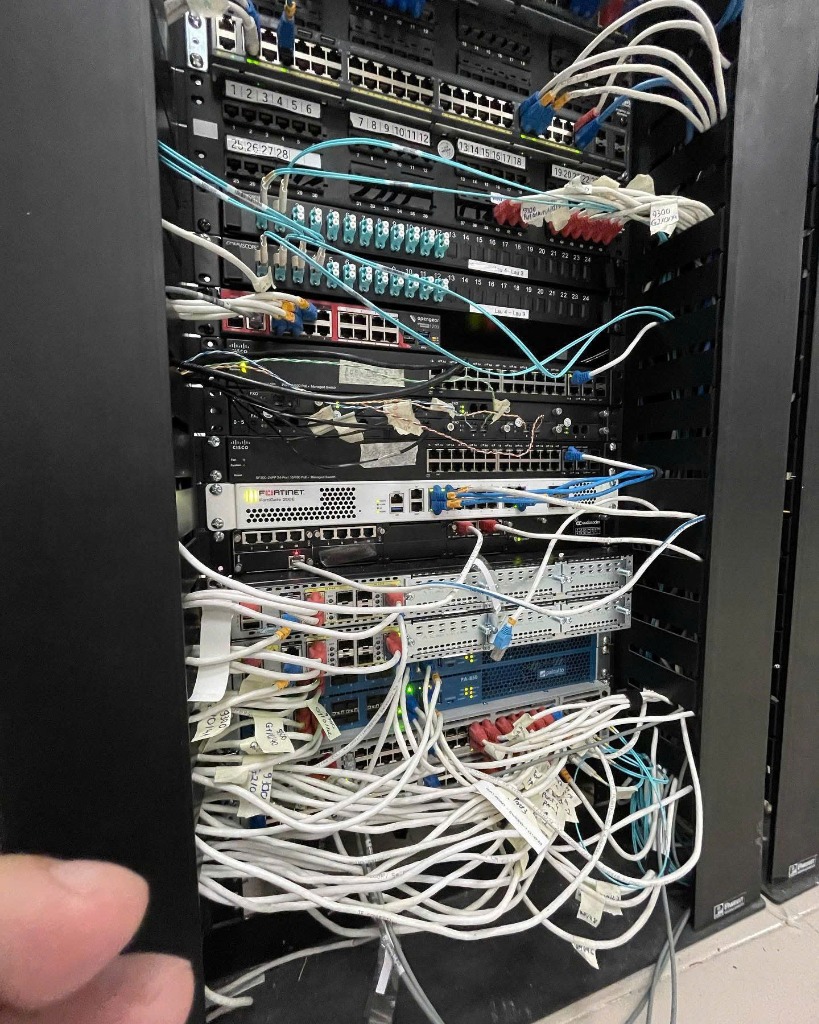
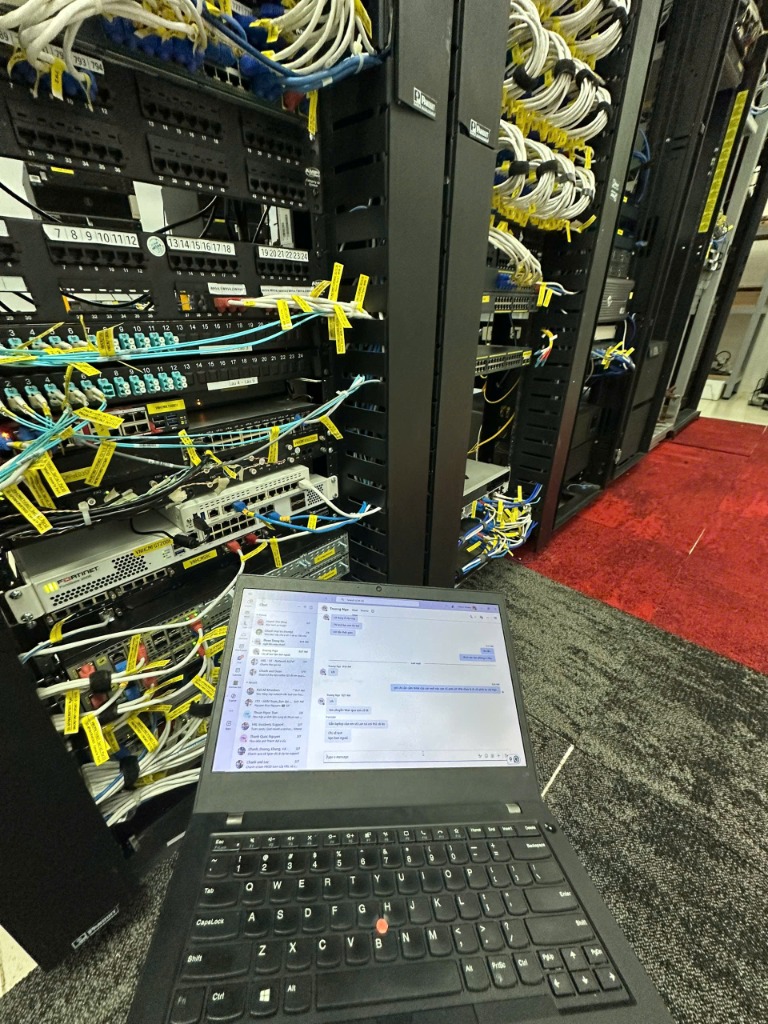
Designed, installed, and administered enterprise on-premises network security and datacenter infrastructure across head offices and factory complexes. Deployed Next-Generation Firewalls (Fortinet FortiGate, Palo Alto Networks PA-850) and Cisco routing/switching to enforce zero-trust network segmentation. Established resilient IPsec Site-to-Site VPN connections between multi-site branches and cloud environments, alongside secure SSL-VPN with MFA for remote users. Managed server racks, structured cabling, VMware ESXi virtualization clusters, and enterprise Microsoft 365 environments.
Built using Fortinet FortiGate, Palo Alto PA-850, IPsec Site-to-Site VPN, SSL-VPN (Remote Access), Cisco Routing & Switching, Network Security (IDS/IPS), VMware ESXi, VLAN & Subnetting
- Next-Gen Firewall Deployment: Configured and managed Fortinet FortiGate (200E) and Palo Alto Networks (PA-850) NGFWs with active IDS/IPS, antivirus, and web filtering policies
- VPN Connection Architecture: Designed and implemented high-availability IPsec Site-to-Site VPN tunnels between HQ, remote factories, and cloud datacenters
- Secure Remote Access: Deployed SSL-VPN with Multi-Factor Authentication (MFA) and granular role-based access control for remote workforce
- Cisco Switching & Routing: Structured core/distribution switching, VLAN segmentation, inter-VLAN routing, and 802.1Q trunking
- Datacenter & Server Rack Operations: Managed server rack mounting, fiber-optic/twisted-pair patch cabling, PDU power distribution, and physical server maintenance
- Virtualization & Systems: Administered VMware ESXi clusters, Microsoft 365 tenant, and VoIP PBX systems ensuring 99.9% uptime
If you're curious, feel free to explore:
Gallery